
Compliance audits make people nervous for a reason. They arrive with a request list, a timeline, and the quiet implication that something will be found.
Something usually is. Not because the business is badly run, but because regulatory requirements accumulate quietly over years while nobody is formally tracking them. A registration that was never updated after the office moved. A register that stopped being maintained when the person responsible left. A filing requirement that kicked in when headcount crossed a threshold two years ago.
The businesses that get through audits comfortably are not the ones with perfect records. They are the ones who knew what the gaps were before the auditor did.
This guide covers what actually happens during a compliance audit, what gets asked for, and how to prepare so the process produces a clean report instead of a long remediation list.
What a Regulatory Compliance Audit Actually Examines
A compliance audit is not a financial audit. It is not checking whether your numbers add up. It is checking whether your operations align with the laws, regulations and industry standards that apply to your business.
That scope is broader than most companies expect. It typically covers statutory registrations and whether they remain current, filing history across applicable laws, maintenance of mandatory registers and records, internal controls governing those processes, and whether the organisation has a mechanism for tracking regulatory change.
The last point is the one businesses rarely anticipate. Auditors increasingly want to see not just that you are compliant today, but that you have a process for staying compliant when the rules change. A business that happens to be compliant through good luck receives a different assessment than one that is compliant by design.
The Four Phases of a Compliance Audit
Understanding the structure helps, because preparation is different at each stage.
Phase One: Planning
The audit scope is defined, applicable regulations are identified, and previous audit findings are reviewed. This is where the auditor determines which laws apply to your specific operations, which is not always obvious for businesses operating across multiple states or industries.
What you should do: Provide an accurate picture of your operations. Understating scope at this stage does not reduce exposure, it just produces an audit that misses things you will have to deal with later anyway.
Phase Two: Fieldwork
Evidence is collected through document review, stakeholder interviews and process observation. This is the longest phase and the one that reveals most findings.
What you should do: Have documents organised and accessible before this begins. Audits extend by weeks when teams are hunting for files, and extended audits cost more and disrupt more.
Phase Three: Reporting
Findings are compiled into a report identifying compliance levels, specific issues and recommended corrective actions.
What you should do: Engage with the draft before it is finalised. If a finding reflects a misunderstanding of your process, that is worth correcting while the report is still open.
Phase Four: Follow Up
Corrective actions are implemented and their effectiveness is reassessed.
What you should do: Treat this as the actual point of the exercise. An audit report that sits unactioned is an expensive document that proves you knew about a problem and did nothing. Our regulatory compliance audit and management services cover this phase specifically, because findings without remediation create more risk than no audit at all.
What Auditors Ask For First
Across most compliance audits in India, the same categories of documentation come up early.
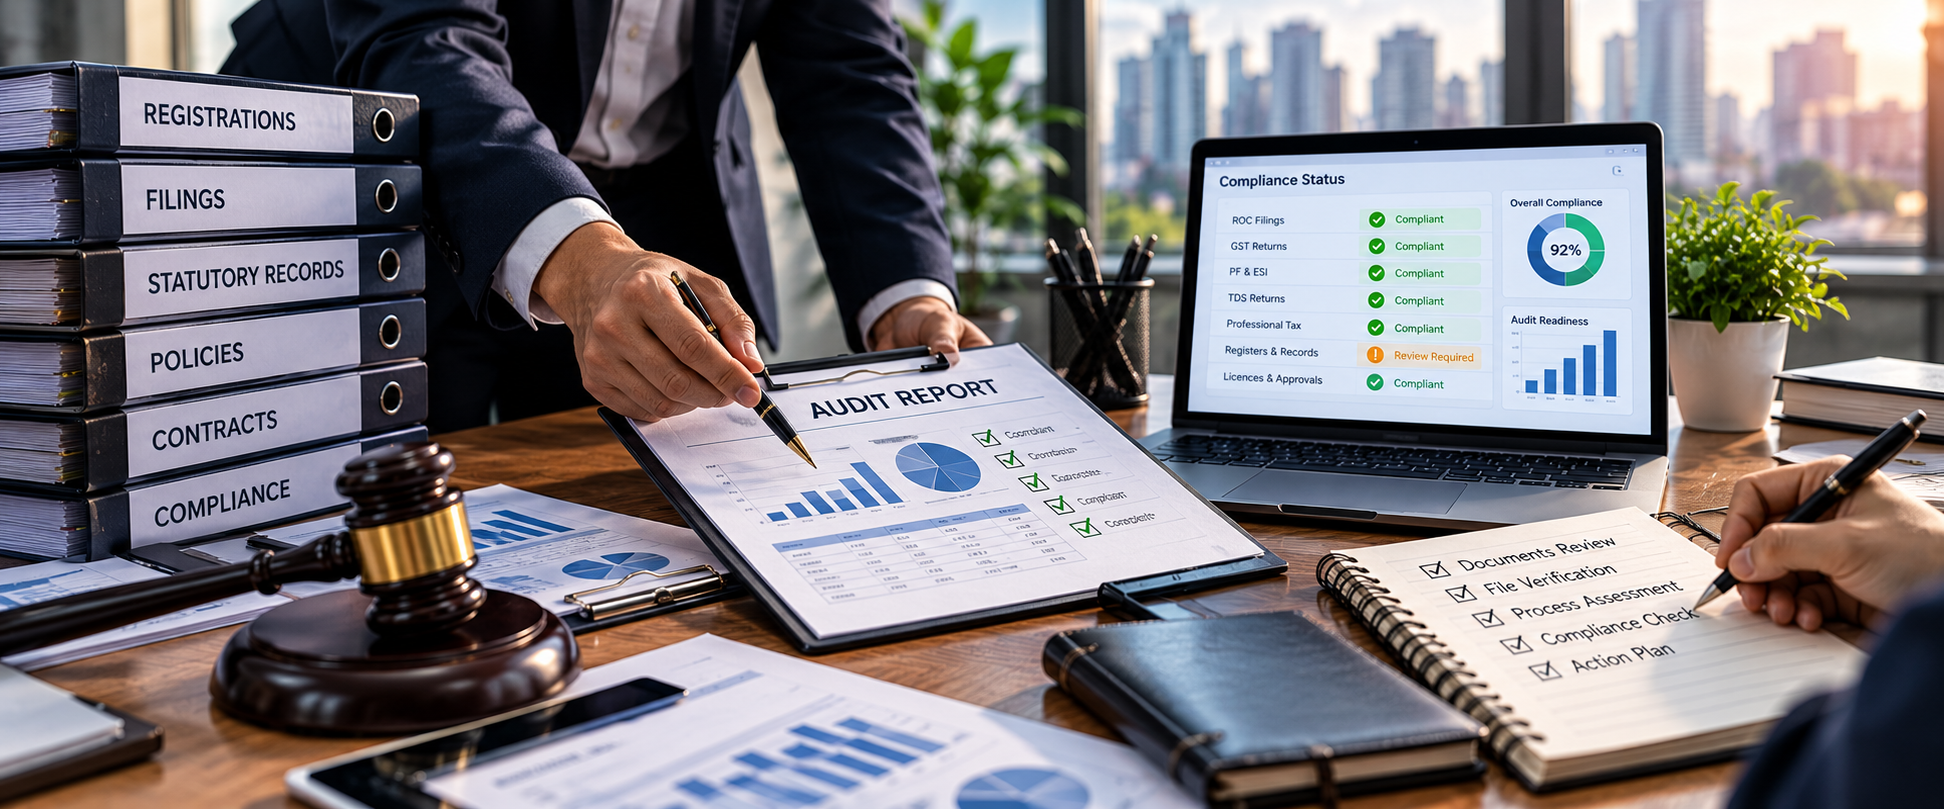
Registration certificates. Incorporation documents, GST registration, PF and ESI codes, professional tax registration, Shops and Establishments registration, and any industry specific licences. Auditors check not just that these exist but that the details on them match current reality. An address that no longer matches your operating premises is a finding.
Filing history. Returns filed under each applicable statute for the review period, with acknowledgements. ROC filings including AOC-4, MGT-7 and DIR-3 KYC. GST returns. TDS returns. PF and ESI challans and returns.
Statutory registers. Register of members, register of directors, minutes of board and general meetings, register of charges, register of wages, attendance and leave records. These are often the weakest area because maintaining them requires continuous discipline rather than periodic effort.
Contracts and agreements. Employment contracts, vendor agreements, client agreements, lease deeds. Auditors look for whether contracts exist at all, whether they are signed, and whether they contain terms that create compliance obligations the business is not meeting.
Policies and internal controls. Documented procedures for the processes that generate compliance obligations. Who approves what, who has access to what, and how exceptions are handled.
The Findings That Come Up Most Often
Certain gaps appear repeatedly, and they are worth checking before an auditor arrives.
Registrations not updated after operational changes. The company moved premises, added a branch, or changed directors, and the corresponding registration was never amended.
Multi state obligations missed. A business headquartered in one state with employees in another frequently misses professional tax, labour welfare fund or state specific registration requirements in the second state.
Registers maintained in form but not substance. Board meeting minutes that are signed but record meetings that did not substantively occur, or wage registers that are reconstructed at year end rather than maintained monthly.
Threshold triggers unnoticed. Headcount crossed the PF or ESI threshold mid year and registration was never obtained. Turnover crossed a GST or audit threshold and the corresponding requirement was not triggered internally.
Contract gaps with related parties. Transactions with directors, group entities or related parties conducted without the documentation or approvals that company law requires.
No regulatory change mechanism. Nobody is formally responsible for tracking amendments, so the business is compliant with the rules as they existed when the process was designed.
Preparing Properly: A Working Sequence
Preparation is more effective when it follows a sequence rather than attacking everything simultaneously.
Start by mapping what applies to you. List every statute, registration and filing obligation relevant to your operations across every state you operate in. This map is the foundation for everything that follows, and most businesses have never formally created one.
Next, verify current status. For each item on the map, confirm the registration is valid, current and correctly detailed. This step alone surfaces a meaningful share of findings.
Then reconstruct the filing trail. Compile acknowledgements for every return filed during the review period. Gaps here are easier to address proactively than to explain during fieldwork.
Review your registers honestly. If a register has not been maintained contemporaneously, note it rather than backfilling it. Reconstructed records are usually identifiable and create a credibility problem that extends beyond the original gap.
Finally, document your controls. Write down who is responsible for each compliance obligation and what the process is. If this does not exist in writing, creating it is itself remediation work that an audit would otherwise flag.
Where Specialist Support Makes a Difference
Internal preparation has a natural limit. The people who built the processes are not well positioned to identify where those processes fall short, and the knowledge required spans company law, labour law, tax law and industry specific regulation simultaneously.
This is where an independent review ahead of a formal audit pays for itself. ACATL conducts compliance risk assessments that identify exposure before it becomes a finding, covering regulatory applicability analysis, internal controls evaluation, and regulatory change management.
The work frequently connects to adjacent areas. Payroll generates a large share of statutory obligations, and businesses often address compliance and payroll outsourcing together so the obligations are managed at source rather than audited after the fact. Where books and records are the issue, accounting outsourcing resolves the underlying cause. Where contracts and documentation are the gap, our legal assistance team handles drafting and review. Where certification is required, assurance and attestation provides it.
Businesses at an earlier stage often find that intellectual property is the overlooked item. Trademark registration and copyright registration rarely appear on a statutory compliance checklist, but unprotected brand assets represent a real commercial exposure that surfaces at exactly the wrong moment, usually during due diligence or fundraising.
The Case for Auditing Before You Have To
Most compliance audits happen because something forced them. An investor is conducting due diligence. A regulator has raised a query. A client has made compliance certification a contractual condition.
Audits conducted under that pressure are the most expensive kind, because findings have to be remediated against someone else’s timeline. Audits conducted voluntarily, before anyone is asking, let you fix problems at your own pace and at a fraction of the cost.
The businesses that treat compliance as an ongoing function rather than a periodic emergency spend less on it overall. That is not an argument about ethics. It is simply what the arithmetic shows.
Getting Started
If you are unsure where your organisation stands, three questions will tell you most of what you need to know. Do you have a documented list of every compliance obligation that applies to your business? Can you produce acknowledgements for every statutory filing from the last two years? If an inspector asked for your statutory registers tomorrow, would they be complete?
Any uncertainty in those answers is worth addressing before someone else identifies it.
ACATL has supported businesses across Delhi NCR for over twenty three years with compliance audits, governance frameworks and ongoing regulatory management. Contact our team for an assessment of your current compliance position.